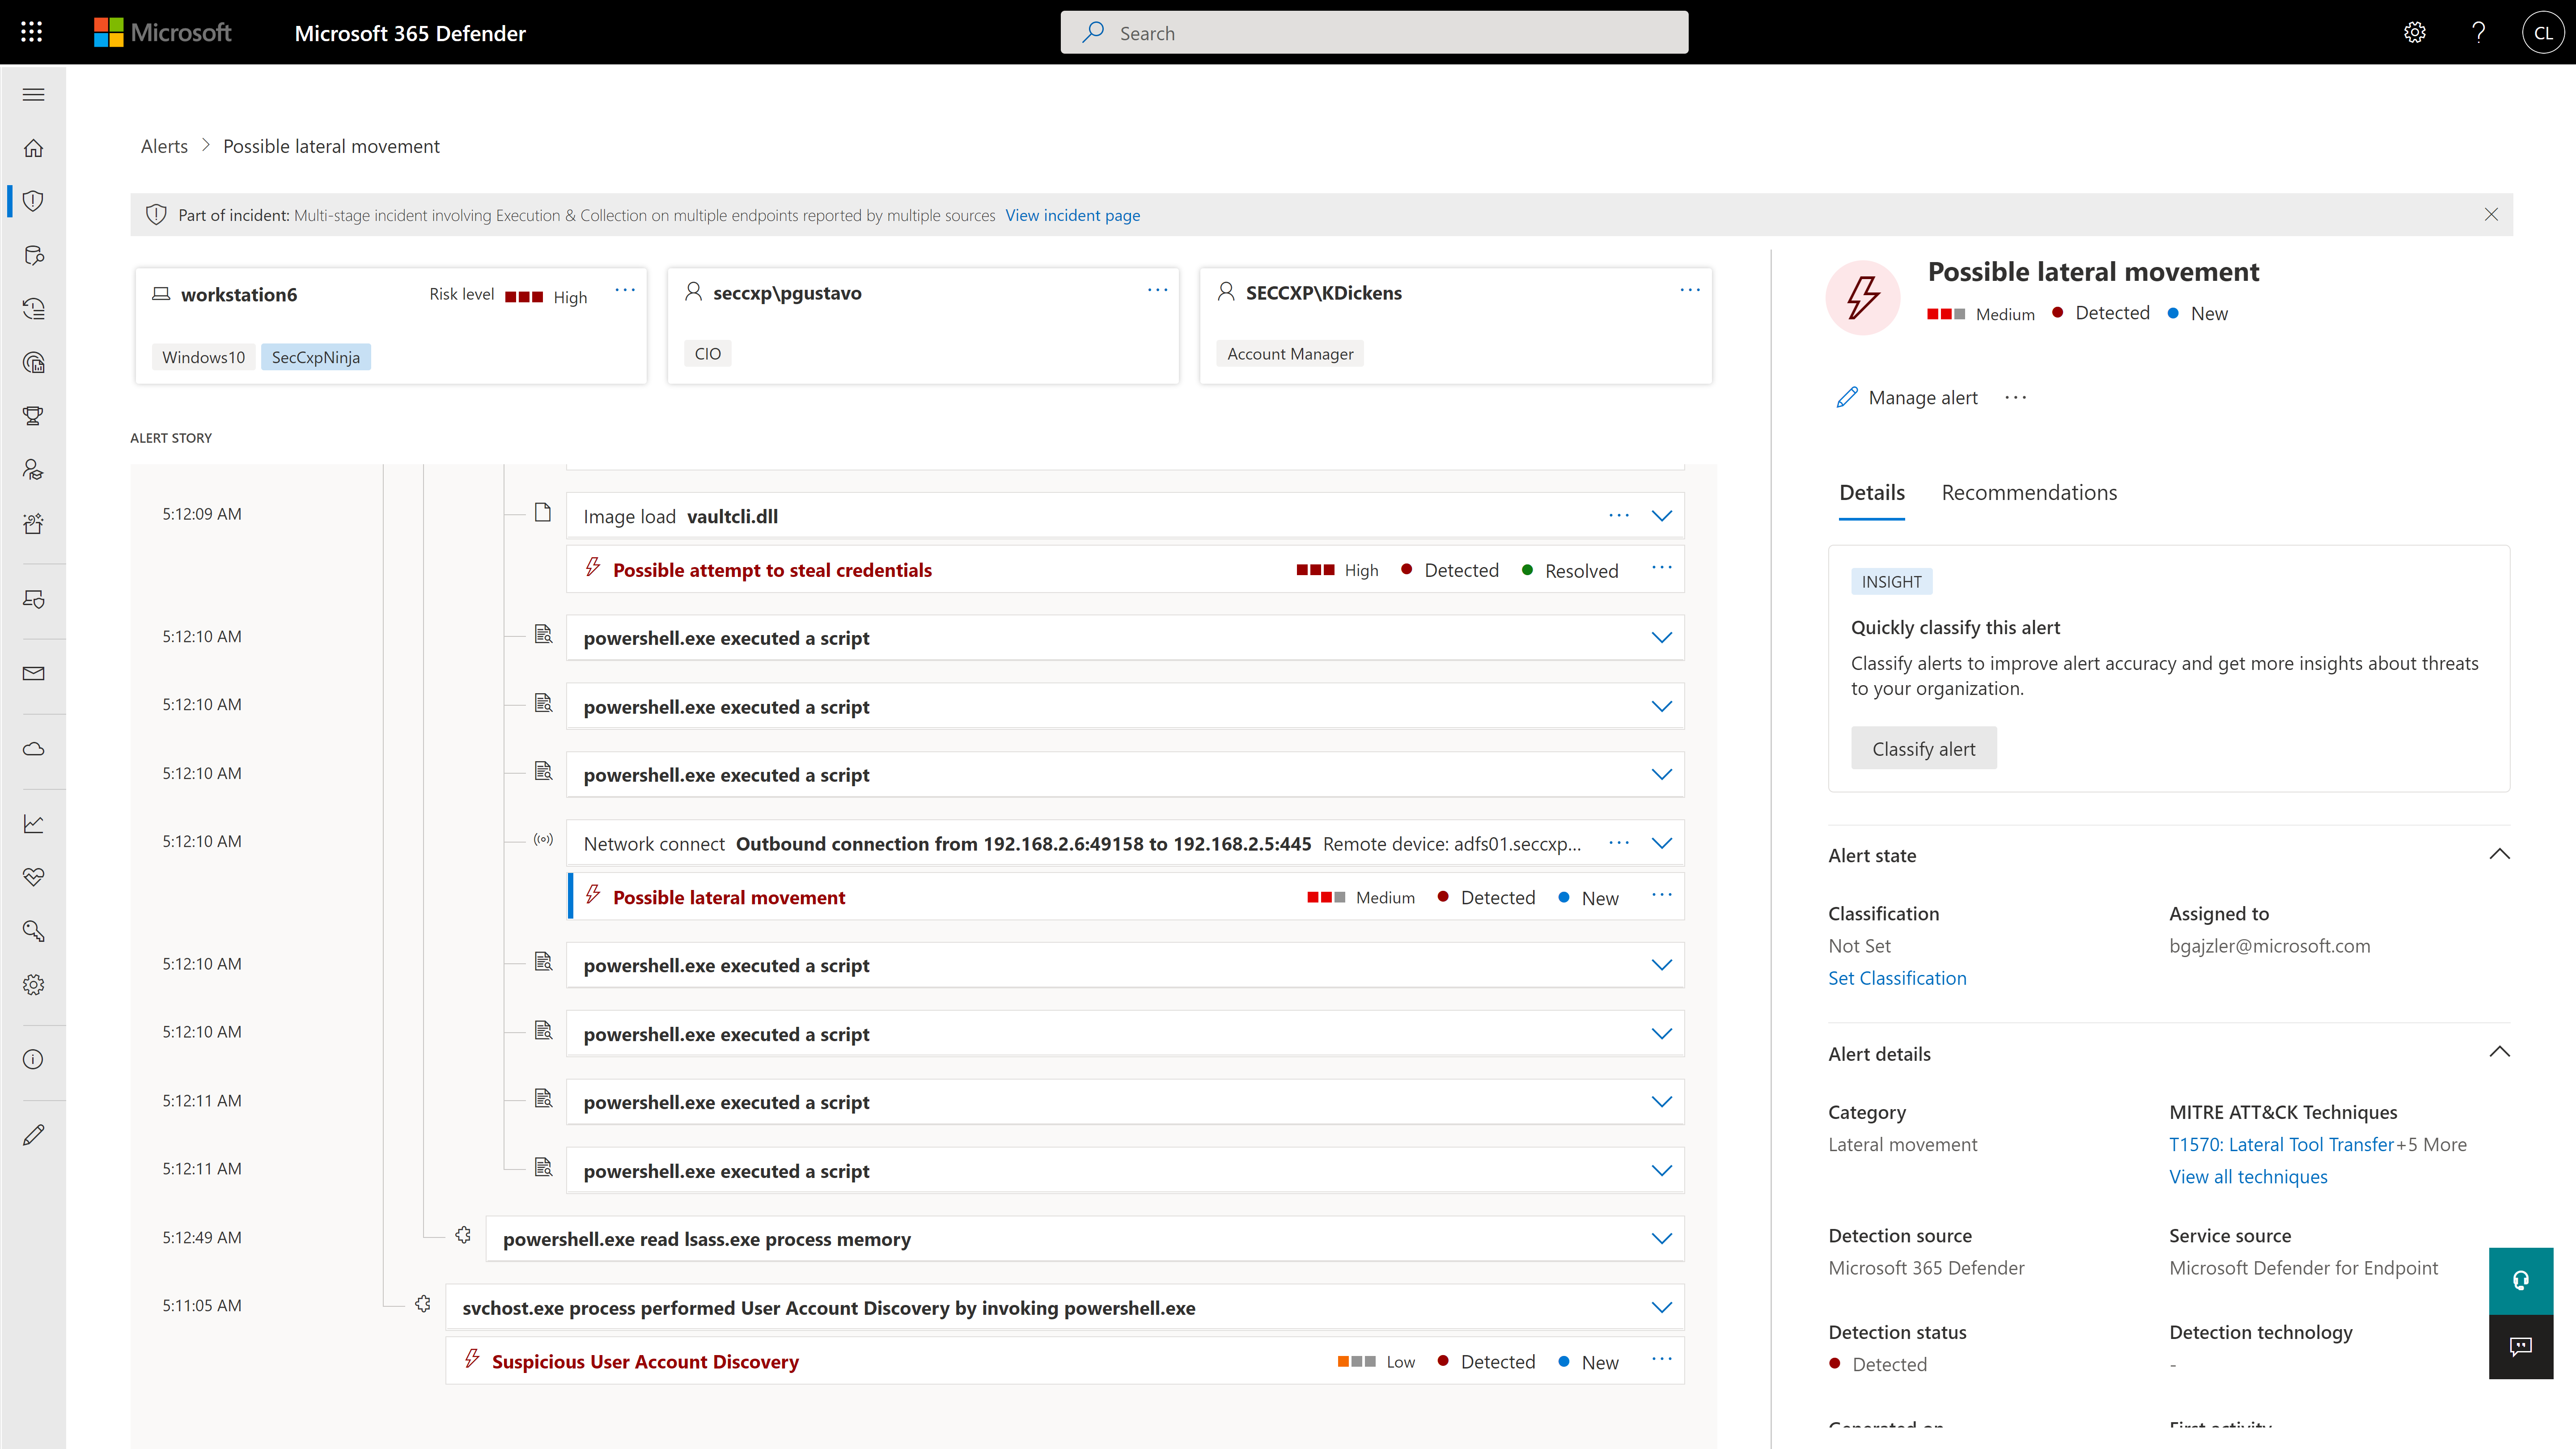
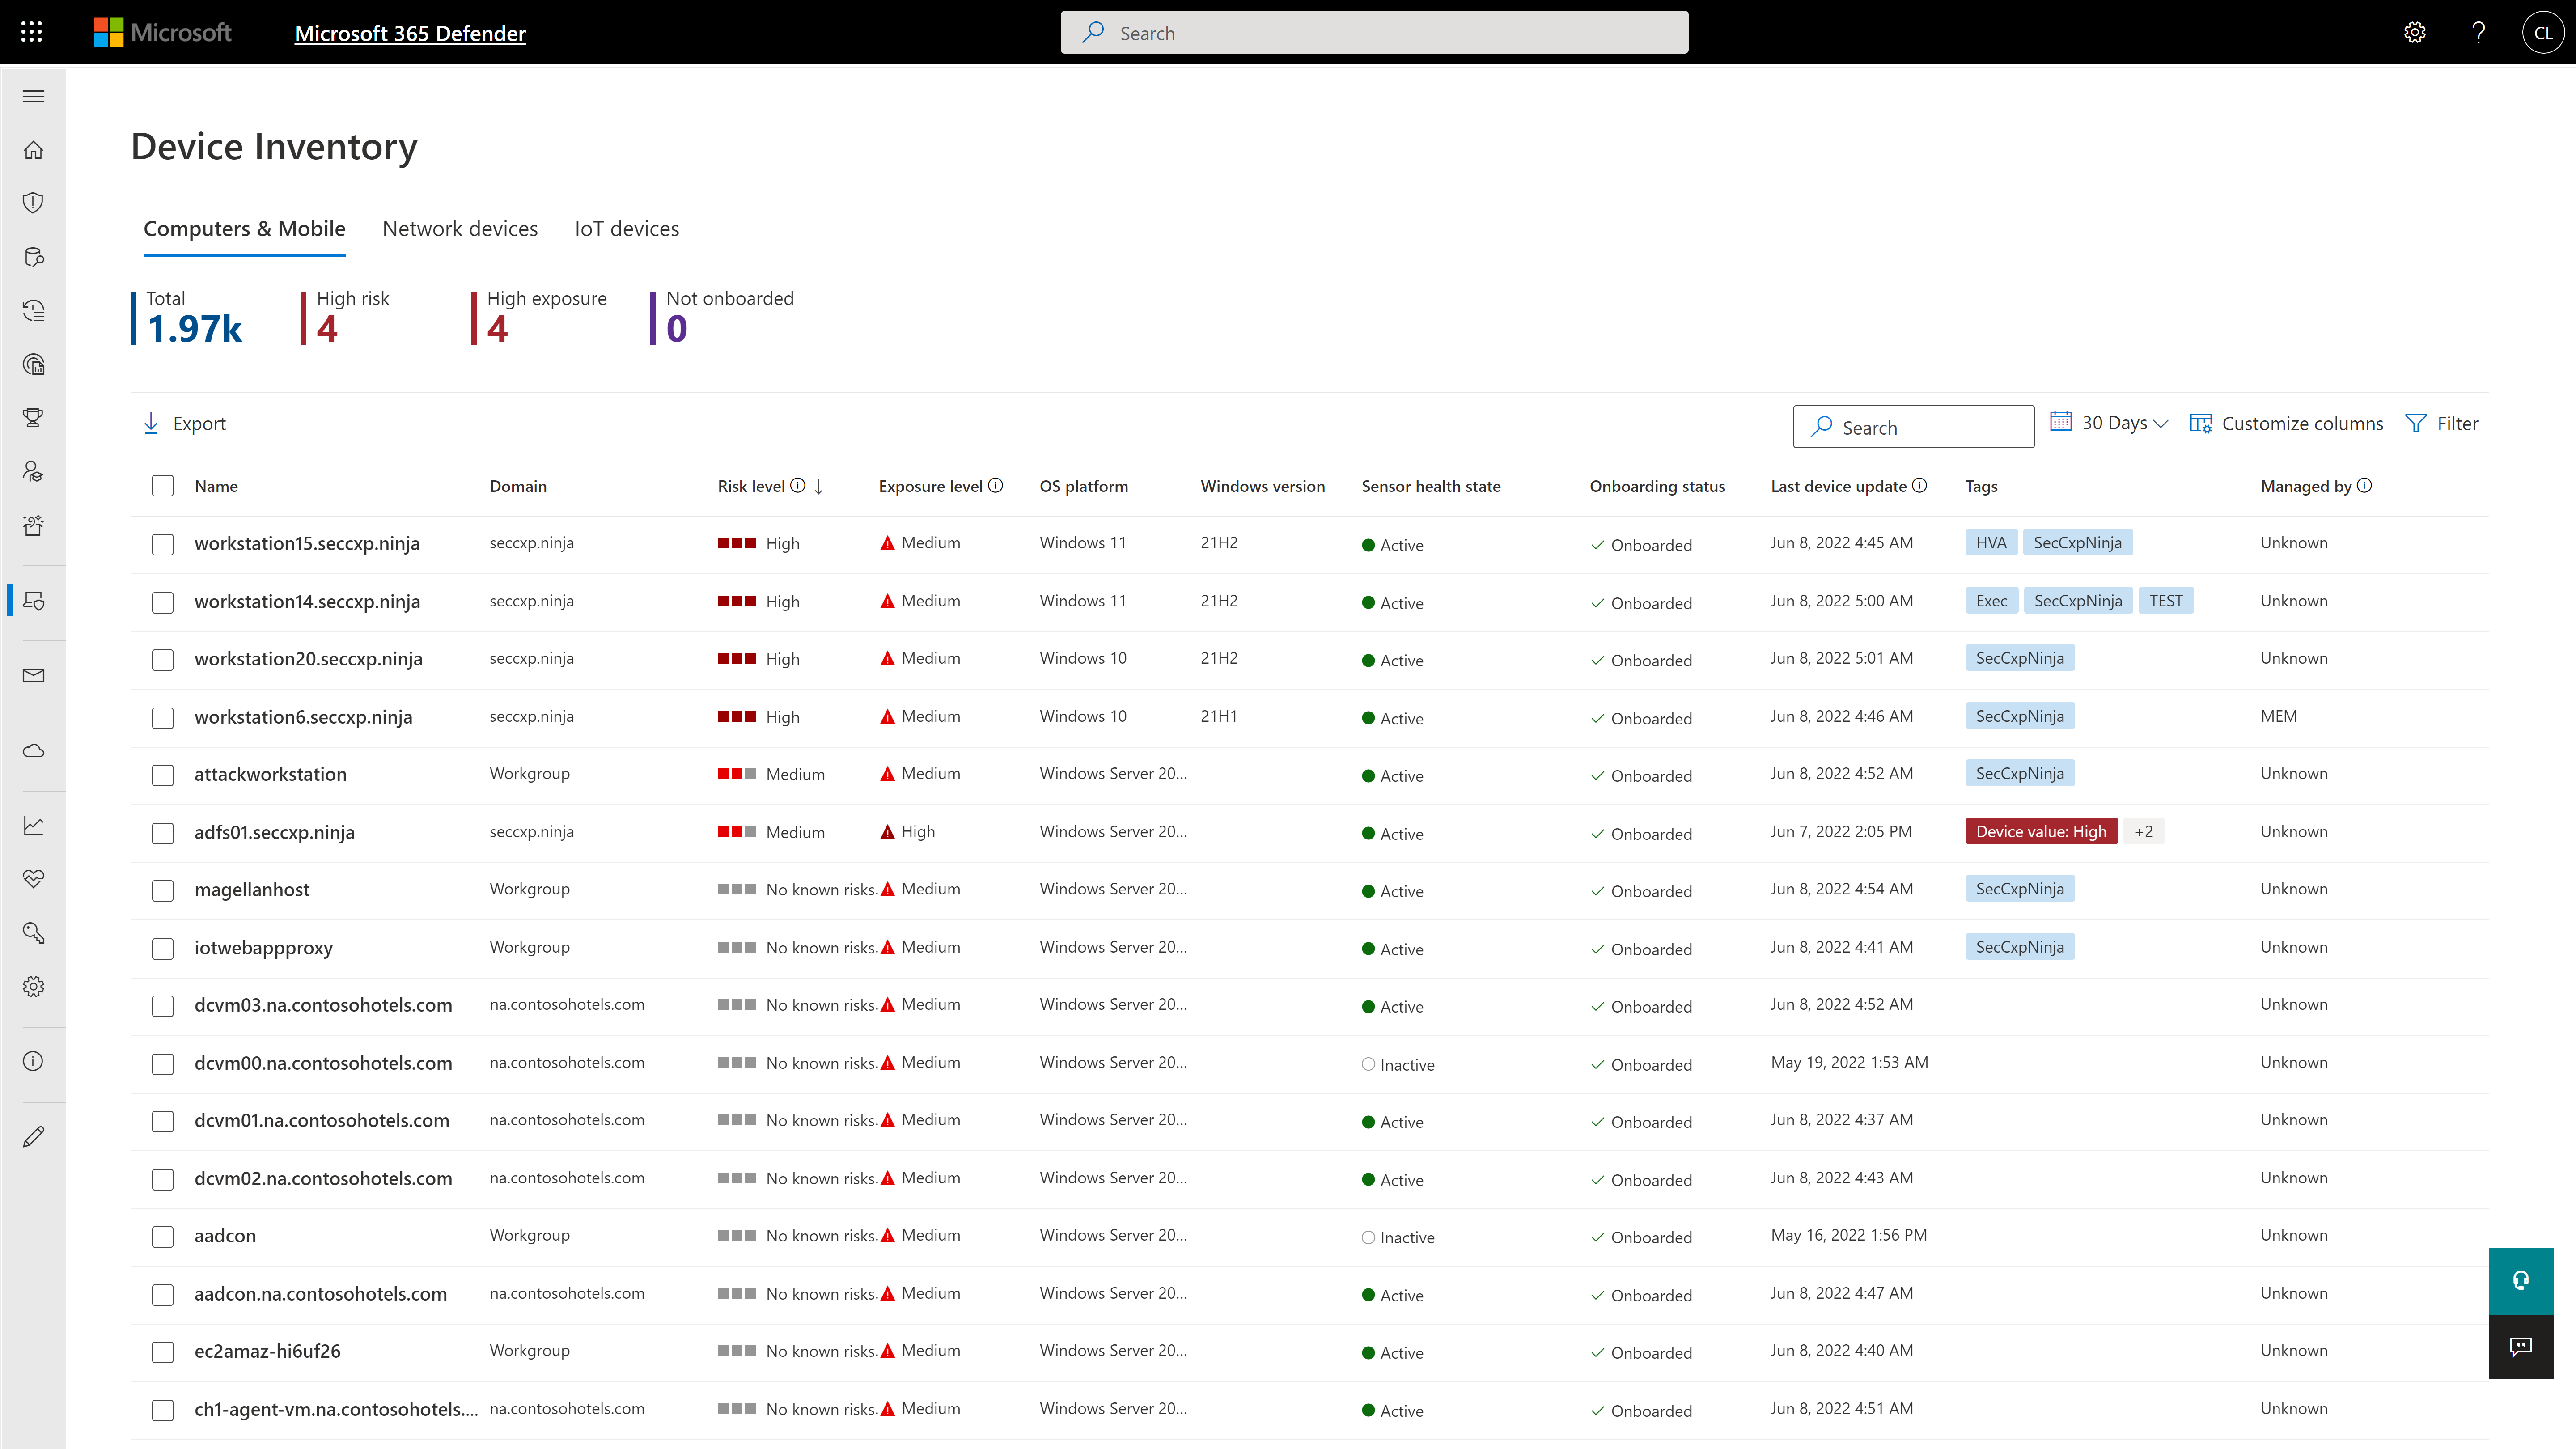
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Consultant in Information Technology (10,001+ employees)
Use Cases and Deployment Scope
In our organization, we use Microsoft Defender for Endpoint to protect against malware, phishing, and other advanced threats. It provides real-time threat detections and automated remediations. This application assists us in improving endpoint compliance and centralized control.
Pros
Endpoint detection and response.
Real time threat detection.
Centralized dashboard.
Role-based access.
Cons
High CPU usage, the application should be lighter.
Improvement needs in UI.
Rules customization in limited.
Mobile support is not as good as a desktop application.
Return on Investment
Strong Microsoft ecosystem.
Integrating multiple security tools.
Threat detections and remediations.
Licensing is expensive.
Usability
Return on Investment
In our organization, we primarily focus on the Microsoft ecosystem. We manage approximately 20,000 endpoints, such as laptops and virtual servers. Although we have Mac & Linux, it's very limited, as the majority of our infrastructure is based on Windows.
Alternatives Considered
Trellix Endpoint Security ENS and Cisco Secure Endpoint
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
IT Engineer in Information Technology at Carolina West Wireless (51-200 employees)
Use Cases and Deployment Scope
We used Defender to replace Sophos. Being included as part of the Microsoft 365 package saved us the entirety of the cost of the previous provider. It also provides significantly more detailed security insights into our devices. Dashboard scores are used to help proactively respond to threats. The software also includes threat assessment to see all of the vectors an attacker would use.
Pros
Dashboard for threats.
Ease of installation.
Rapid response to threats.
Cons
PC reporting often lags behind, so scores remain unchanged longer than desired.
The portal interface changes regularly, moving objects and menus.
It needs a more defined client interface to resemble a traditional third-party antivirus.
Return on Investment
Was able to alert us to a malicious event overnight, tracking the incident end-to-end.
Gives management clear insight into the security footprint of the company.
Saved several thousand dollars a year in 3rd party antivirus costs.
Return on Investment
We are currently deployed to around 200 total PCs and servers. Our PCs are mostly Windows 11 with a few Windows 10 PCs that are in the process of being replaced. Our servers are entirely Windows-based, with most using Server 2019. We are not currently using Defender on mobile devices.
Alternatives Considered
Sophos Managed Detection and Response
Other Software Used
Microsoft Intune, Microsoft Exchange Online Archiving, VMware vSphere
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Founder in Corporate at LetsReflect (1-10 employees)
Use Cases and Deployment Scope
We use Microsoft Defender for Endpoint as an antivirus to protect our systems from different types of malware. It helps us uncover attacks which are happening on our machines. Also, it is useful in getting timely alerts for such attacks.
Pros
Detect attacks
Prevent infection from malware
Provide alerts
Cons
Easy to use management interface
Return on Investment
It has reduced the expert manpower requirement to less than 50% for detection
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cybersecurity Director in Information Technology at Impresoft 4ward (501-1000 employees)
Use Cases and Deployment Scope
It's our primary EDR on client and servers.
Pros
It's particularly good to log and integrate with the Microsoft Security stack and to protect and have details on what happening on devices.
Cons
difficult to use Live Response
quite difficult to install it on legacy operating system.
Return on Investment
As a partner and as a reseller, we recommend it to every customer. The problem of the challenge here is that other EDRs are sold as a lower price and not every customer understands the value of having this type of application and this type of features on their environment.
Return on Investment
We are protecting 250 Windows clients and 150 windows and Linux Servers
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cybersecurity Senior Engineer in Information Technology at Maureen Data Systems (MDS) (201-500 employees)
Use Cases and Deployment Scope
First thing I use in this product for no more than the employee devices, right? One of the key features that the for Endpoint is giving us is the vulnerabilities for those devices and also no more what are the vulnerabilities score that we have in the company. It's helping us to address those vulnerabilities, giving us all the recommendations and really like how this has been working for us to know more how we expose it to our devices to specific attacks.
Pros
I think the detection part is one of the things that the Defender for Endpoint does very well, it's very faster. I really like it how you can do the detection and response and the remediations that they have depending on the license of course. But yeah, I think those areas are most of the best for the technical response is very good on that.
Cons
I think one of the cons that I don't like about this is for example when you integrate with Defender antivirus, so how quickly this actual product does like you depending for another products like Microsoft intern for Deploy the policy and then waiting for the device can be synchronizing. I think that is something that I see more room for improvement that even the customer that have been working with, they are facing some kind of issues like I adding this policy but I need to wait 5 minutes, 10 minutes because this is security needs to be out faster. I think those are the things that I can talk about the account on that piece.
Return on Investment
I think the positive is the investment, right? So even if you have your license because you're using a licensing environment and just to have it there, my speech is always regarding using what you have and if you have a good tool that has been categorizing as one of the best tools, so why don't use it, right? So my thing, I think the positive thing is use it working because it's integrated, it's native for the consoles and other products and I think that will be the best impact that I will be provided to customer.
Return on Investment
In my company, yes. Currently we have 200, but I have been working with companies that they have more than 3000 devices working with Different For. We use all platforms.
Other Software Used
Microsoft Entra ID, Microsoft Defender for Cloud Apps
Usability
Microsoft Defender for Endpoint Alternatives
Products similar to Microsoft Defender for Endpoint that may also meet your needs.